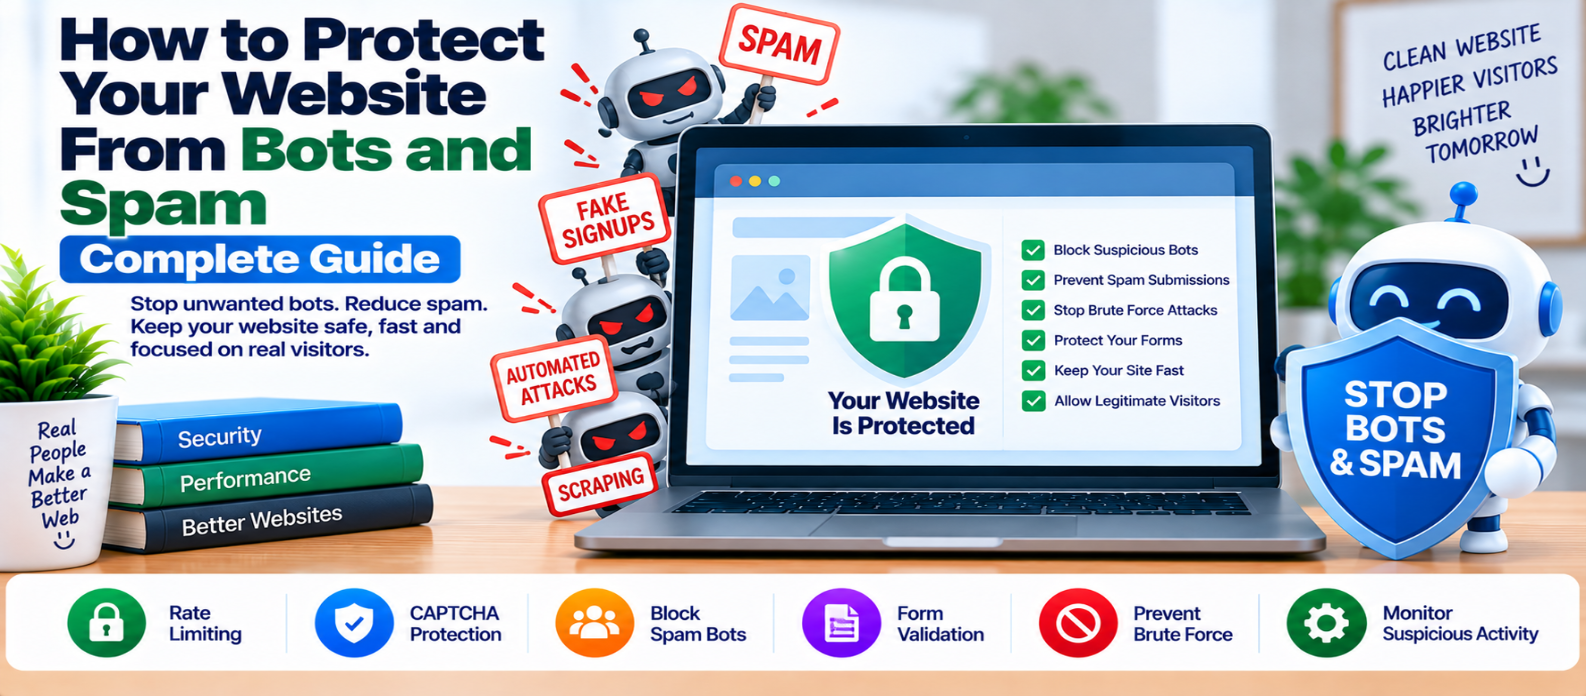
How to Protect Your Website From Bots and Spam: Complete Guide
"Learn how to protect your website from malicious bots and spam using rate limiting, login protection, honeypots, CAPTCHA, server-side validation, WAF controls, API safeguards, monitoring, and layered anti-bot defenses."
How to Protect Your Website From Bots and Spam
Not every bot visiting your website is harmful.
Search crawlers, monitoring systems, accessibility tools, and services you intentionally use may generate automated traffic. The real problem is abusive automation—bots that flood forms, create fake accounts, scrape content aggressively, test stolen credentials, generate spam, or consume excessive server resources.
Effective protection therefore isn't about blocking every bot.
It's about identifying suspicious behavior and making automated abuse harder without frustrating legitimate visitors.
Understand What You're Defending Against
Bot and spam activity can appear in different forms:
Comment Spam
Fake Registrations
Contact Form Spam
Credential Attacks
Aggressive Scraping
Automated Purchases
API Abuse
Resource Exhaustion
Different problems need different controls.
A defense that works well for comment spam may not stop automated login attempts.
1. Add Rate Limiting
Rate limiting restricts how frequently a client can perform certain actions.
For example, a normal visitor probably doesn't need to submit a registration form hundreds of times within minutes.
Apply sensible limits to high-risk endpoints such as:
- Login
- Registration
- Password reset
- Contact forms
- Comments
- Search
- APIs
- Expensive processing operations
Don't necessarily use one universal limit.
A lightweight public page and an expensive API operation have different abuse risks.
2. Protect Login Pages
Automated systems may repeatedly test usernames and passwords.
Useful protections can include:
- Rate limiting
- MFA for sensitive accounts
- Detection of unusual login behavior
- Temporary throttling
- Secure password policies
- Monitoring repeated failures
Avoid permanently locking legitimate users out simply because someone repeatedly attempted to access their account.
Progressive delays or other risk-based controls can often be more practical.
3. Use CAPTCHA Selectively
CAPTCHA or challenge systems can help distinguish suspicious automated activity from human interaction.
However, forcing every visitor to complete a challenge can hurt usability and accessibility.
A better approach is often:
Normal Activity
      ↓
Minimal Friction

Suspicious Activity
      ↓
Additional Challenge
Use challenges where abuse risk justifies them—for example, repeated registrations or suspicious form submissions.
CAPTCHA should be one layer rather than your entire anti-bot strategy.
4. Add Honeypot Fields to Forms
A honeypot is a form field designed to remain unused by legitimate visitors but may be filled by simplistic automated systems.
Conceptually:
Normal User
   ↓
Leaves Hidden Trap Empty
   ↓
Submission Continues

Simple Bot
   ↓
Fills Every Field
   ↓
Suspicious Submission
Honeypots can reduce basic spam without requiring visitors to solve puzzles.
Implement them carefully so they don't interfere with assistive technologies or legitimate form-filling tools.
5. Check Submission Timing
Humans generally need some time to read and complete a form.
A submission arriving almost immediately after the form is served may deserve additional scrutiny.
Timing shouldn't be treated as absolute proof of automation because password managers, autofill, accessibility tools, and fast users can behave differently.
Instead, combine timing with other signals.
6. Validate Everything on the Server
Never rely only on browser-side validation.
Bots can send requests directly to your server without using your webpage.
If a form expects:
Name: reasonable text
Email: valid structure
Message: limited length
validate those requirements again on the server.
Reject malformed, oversized, unexpected, or unnecessary input before expensive processing occurs.
7. Protect Forms Against Repeated Spam
For comment, registration, and contact forms, combine several defenses:
Input Validation
      +
Rate Limiting
      +
Honeypot
      +
Behavior Signals
      +
Challenge When Needed
Layered controls are harder for automated systems to bypass than one simple test.
For user-generated content, moderation and spam classification can provide another layer.
8. Use a Web Application Firewall Carefully
A Web Application Firewall (WAF) can inspect incoming traffic and block or challenge requests matching suspicious patterns.
Depending on the system, it may help with:
- Known malicious request patterns
- Abusive IP addresses
- Excessive request rates
- Suspicious automated behavior
Don't assume a WAF makes vulnerable application code safe.
Your website still needs secure authentication, authorization, input handling, updates, and monitoring.
9. Protect Your APIs
Bots don't need to interact with visible webpages.
They can target API endpoints directly.
API protection may include:
- Authentication where required
- Per-user or per-key limits
- Resource-level authorization
- Input validation
- Request-size limits
- Usage monitoring
- Appropriate quotas
Pay special attention to expensive endpoints. A request that triggers heavy database queries or processing can become a resource-abuse target.
10. Don't Trust User-Agent Strings
A request can claim to be almost anything through its User-Agent header.
Therefore:
User-Agent says:
"Friendly Search Bot"

Does not automatically mean:
Trusted Bot
When verifying important known crawlers, use reliable verification methods appropriate to that service rather than trusting a self-declared name.
11. Be Careful With robots.txt
robots.txt can tell cooperative crawlers which parts of a website you prefer them not to crawl.
It is not an access-control mechanism.
A malicious bot can simply ignore it.
Never use robots.txt to protect:
- Private files
- Administrator pages
- Confidential data
- Restricted APIs
Sensitive resources need real authentication and authorization.
12. Monitor Bot Behavior
You can't manage abuse effectively if you don't know what is happening.
Watch for patterns such as:
- Sudden traffic spikes
- Thousands of requests to one endpoint
- Repeated login failures
- Rapid account creation
- Identical form messages
- Unusual API usage
- Excessive requests from limited sources
- Unexpected bandwidth or server load
Look at behavior over time rather than assuming every unusual request is malicious.
13. Protect Server Resources
Bot protection is also a performance issue.
Automated traffic can consume:
CPU
Memory
Database Connections
Bandwidth
API Quotas
Application Workers
Caching appropriate public content can reduce repeated backend work.
Request-size limits, timeouts, queues, rate limits, and resource controls can also prevent one type of request from consuming disproportionate capacity.
14. Avoid Blocking Too Aggressively
An overly aggressive anti-bot system can block:
- Search crawlers
- Users behind shared networks
- Accessibility tools
- Monitoring services
- Privacy-conscious visitors
- Legitimate API clients
Instead of immediately blocking every suspicious request, consider graduated responses:
Normal
  ↓
Allow

Unusual
  ↓
Monitor / Throttle

Suspicious
  ↓
Challenge

Clearly Abusive
  ↓
Block
This reduces unnecessary friction while still responding strongly to obvious abuse.
Bot and Spam Protection Checklist
Review whether your website has:
-
Rate limits on sensitive endpoints
-
Strong login protections
-
MFA for important accounts
-
Server-side form validation
-
Honeypots where appropriate
-
CAPTCHA or challenges used selectively
-
Spam moderation for user-generated content
-
API abuse controls
-
Request-size limits
-
Appropriate caching
-
WAF rules where useful
-
Monitoring for unusual traffic
-
Logging for repeated failures
-
Real access control for private resources
-
Legitimate bots considered before blocking
-
Anti-bot rules periodically reviewed
Conclusion
Protecting a website from bots and spam isn't about identifying one magical setting that stops automation.
A stronger strategy uses several layers:
Observe Traffic
      ↓
Validate Requests
      ↓
Limit Abuse
      ↓
Detect Suspicious Behavior
      ↓
Challenge When Needed
      ↓
Block Clear Abuse
      ↓
Monitor and Adjust
Start with secure server-side validation and rate limiting. Add form-specific protections, authentication controls, API safeguards, monitoring, and carefully targeted challenges according to your site's actual abuse patterns.
The objective isn't to create the most aggressive bot protection possible.
It's to make abuse expensive and ineffective while keeping your website fast and accessible for legitimate visitors.
Get a Free Access To 200+ Free Tools:
|
Home Page |
|
|
Calculator Tools |
|
|
Text & Converter Tools |
|
|
PDF & Image Tools |
|
|
Games & Developer Tools |
|
|
Resume Builder |